 Dailytech
Fridge Hack Hit 700 Supermarkets Through Neglected Devices
Security·October 16, 2026
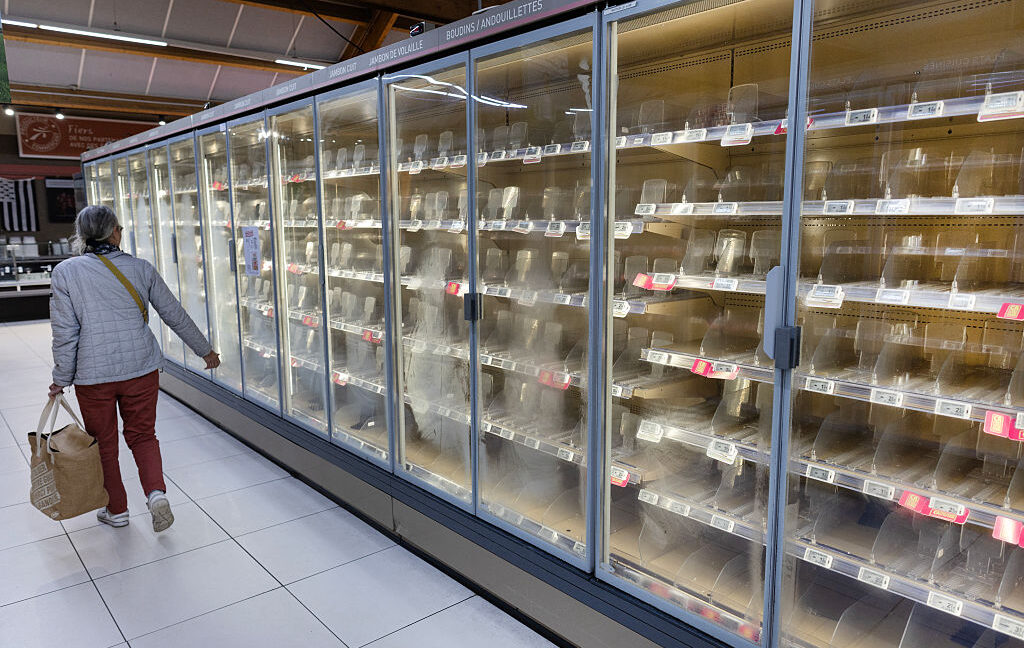
A cyberattack that reached roughly 700 supermarkets did not need sophisticated tools to get in. According to the reporting behind this story, the intruders went after outdated refrigeration equipment that was reachable from the internet, and the damage ran into the millions. Some of the incidents reportedly sparked fires, turning a digital intrusion into a physical safety problem for stores and their staff.
The core failure is basic. Commercial cooling systems are often built to run for many years, and their controllers and management interfaces are frequently left unpatched because replacing them is expensive and nobody wants to take a cold chain offline. When those devices sit directly on the public internet, with weak or default credentials and no network segmentation, they become easy targets. Once an attacker controls a unit, they can change temperatures and settings in ways the operator never intended.
For retailers, the lesson goes beyond one chain. Many grocers run dozens of connected systems that were never designed with security in mind, from refrigeration and HVAC to point-of-sale hardware. Security teams routinely recommend keeping operational equipment off open networks, putting remote access behind a VPN or a managed gateway, changing default passwords, and maintaining an accurate inventory of what is actually connected. Those steps are inexpensive compared with the cost of spoiled stock, store closures and fire damage.
The episode also points to a gap between IT and facilities teams. Equipment that keeps food cold often falls outside the security budget and the patch schedule, which leaves it quietly exposed for years. Until those systems are treated as part of the company's security perimeter, similar incidents are likely to keep surfacing.
Reporting based on an external source.